Whitepaper · Manufacturing and operational technology
Designing secure IT–OT access without disrupting production
A conceptual architecture and operating model for controlled vendor support, engineering oversight and safe closure.
Companion research reportRemote vendor access to production systems: where control needs verification EFF-RR-2026-005
Research cut-off: 11 November 2026 · Proposed implementation framework; not empirically validated.
1Executive summary
Manufacturers need specialist support for equipment that may remain in service for many years. Remote connectivity can make that support more responsive, but it also creates a path by which external identities, devices and software interact with production systems.
The design challenge is to make support possible within an understood operational boundary. The plant should know who can connect, which equipment they can reach, what work is authorised, who is supervising and how the route can be closed. Those conditions must remain meaningful when equipment has limited security capabilities or support is required urgently.
This whitepaper proposes an architecture and operating model for controlled vendor support. It combines a managed access path with task-specific authorisation, target restrictions, engineering change control and evidence of closure. It also examines the access platform itself as a dependency that can fail or be compromised.
Design principles
Bind support authority to a person, task, target and operating window.
Integrate remote work with engineering verification and safe closure.
Validate the access platform, alternate routes and exceptions as part of the design.
What this means
- Leadership
- Assign plant ownership for one vendor support route and its safe operating conditions.
- Security and technology
- Validate material technical assumptions, preserve evidence and state the boundaries of what was examined.
- Service and operational owners
- Own acceptance criteria, unresolved work and the review of changes that could invalidate an earlier decision.
2Scope and questions
Research questions
- How can the proposed framework be applied proportionately to one service and validated before broader adoption?
- Which claims are supported by the reviewed sources, and which proposed practices require local validation?
In scope
- Manufacturing and operational technology service and security decisions, with a Singapore-focused editorial lens.
- Purposively selected official primary sources checked on 11 November 2026.
- Qualitative analysis, hypothetical examples and proposed assessment practices.
Out of scope
- Incident prevalence, statistical estimates of risk and regional attack rates.
- Client assessments, laboratory evaluation and measured control effectiveness.
- A complete legal or regulatory compliance determination.
3Methodology
This is a purposive review of the primary sources listed below, selected for direct relevance to the research question and authoritative provenance. It is not a systematic literature review; no completeness or exhaustive search claim is made.
Source guidance was compared with the decision questions in this publication. Analytical conclusions and proposed practices were developed separately from source descriptions. Examples are hypothetical. No interviews, client records, clinical workflows, production equipment or supplier controls were examined.
Singapore's OT Cybersecurity Masterplan 2024 provides strategic context for secure deployment across the equipment lifecycle. It includes resilience beyond critical information infrastructure. CSA: OT Cybersecurity Masterplan 2024.
NIST's OT security guide addresses remote access justified by business need, operating constraints and the ability to disconnect remote access without adversely affecting OT operations. NIST SP 800-82 Rev. 3.
NCSC guidance promotes centralised, repeatable connectivity, with a managed route through an OT demilitarised zone as an example. NCSC: Secure connectivity, Principle 3.
CISA's OT mitigation factsheet recommends protecting remote access and limiting it by asset and role. CISA: Primary mitigations for OT.
The proposed architecture, assurance tests and governance model below are original analysis informed by these themes. The sources are guidance rather than evidence that a particular implementation works. Their use here does not establish which regulatory duties apply to an individual plant.
Sources
| Source | How it was used | Reliability |
|---|---|---|
| Cyber Security Agency of Singapore. (2024). Singapore’s Operational Technology Cybersecurity Masterplan 2024. | Singapore strategic context and secure deployment across the OT lifecycle. | Official overview; a strategy, not a universal mandatory control checklist. |
| Stouffer et al. (2023). Guide to Operational Technology (OT) Security. NIST SP 800-82 Rev. 3. | Bounded remote access and disconnect capabilities compatible with OT operations. | Primary technical guidance; relevant remote-access provisions reviewed. |
| UK National Cyber Security Centre. (2026). Secure connectivity principles for OT: Principle 3, Centralise and standardise network connections. | Repeatable managed access architecture and OT boundary pattern. | Primary technical guidance; effectiveness depends on local implementation. |
| CISA and partners. (2025). Primary Mitigations to Reduce Cyber Threats to Operational Technology. 6 May 2025. | Essential remote access, least privilege and IT–OT segmentation. | Official-source indexed text reviewed; direct retrieval returned HTTP 403; used only for visible recommendations. |
Review
Prepared with AI-assisted research and drafting. Source references, content structure, internal links and build behaviour were checked during preparation. No independent subject-matter, clinical, engineering or legal peer review has been conducted.
- Preparation checks: Automated and AI-assisted checks, Source-link, content-structure and build verification; not independent peer review
Data availability
Download the assessment worksheet (CSV) · Download the framework diagram (SVG) · Download the source register (JSON)
Companion report: Remote vendor access to production systems: where control needs verification.
4Proposed framework
Framework component 1
Define the operational purpose before the connection
Proposed · requires local validation
Describe each access use case in operational terms. Separate viewing diagnostic information, collecting logs, changing configuration, updating software and modifying control logic. Engineering should specify the authority and verification appropriate to each activity.
For each use case, identify the target equipment, support organisation, local owner and required tools. Record expected connectivity, timing, file exchange and local participation. Where support software needs broad privileges, make those privileges visible in the approval decision.
An operational requirement should include the consequence of unavailable remote support. The response might be delayed maintenance, local intervention or a controlled production restriction. That consequence helps determine the access platform's availability needs and the acceptable emergency process.
Avoid building a general-purpose path before agreeing its permitted use. A remote desktop into a broad engineering environment can convey much more authority than a narrowly defined diagnostic task requires. Where a broad tool is unavoidable, compensate through scoped reachability, supervision and a reviewed operating boundary.
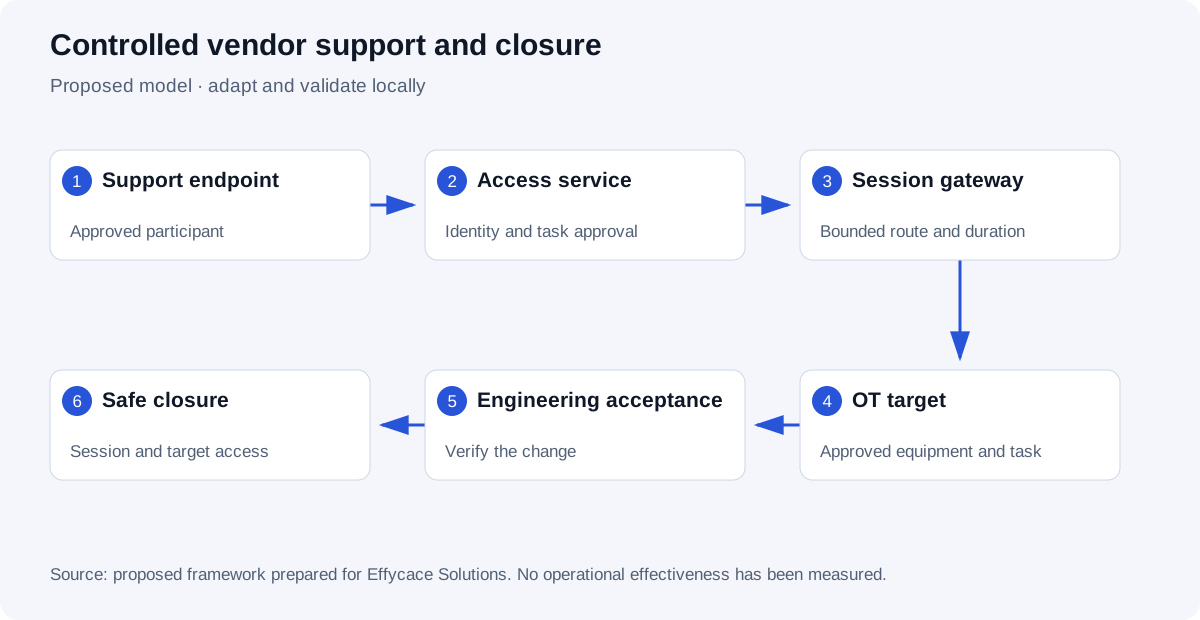
Source: proposed model prepared for Effycace Solutions. This diagram represents analytical relationships and proposed workflow, not observations or measured effectiveness. A textual description is embedded in the downloadable SVG.
Framework component 2
Establish the current routes
Proposed · requires local validation
Create a connection register that includes more than enterprise VPNs. Review supplier-installed devices, cellular links, site-to-site tunnels, remote management tools, cloud relays and temporary commissioning arrangements where present. Discovery should combine engineering knowledge with approved technical evidence.
For each route, record its endpoints, owner, operational purpose, authentication, accessible systems and closure method. Include the evidence date and unresolved assumptions. A route shown on an old drawing should not automatically be treated as the route currently in use.
Validate connectivity through methods suitable for the equipment. Do not introduce scanning, agents or configuration changes into production merely to complete the register. If a fact cannot be confirmed safely, mark it as unknown and plan a controlled verification opportunity.
The register should support decisions about consolidation and exceptions. Some legacy routes may require a staged replacement because they support contractual or technical functions. Document the interim controls and retirement conditions rather than leaving the route outside the managed process.
Framework component 3
A conceptual access architecture
Proposed · requires local validation
The proposed model separates the external user, the access-control service and the production target. Its intended flow is:
Approved support endpoint → authenticated access service → controlled session gateway → authorised OT zone and target.
A separate controlled process handles file transfer. Administrative access to the gateway and policy platform is restricted and reviewed independently of ordinary vendor use. The exact deployment, including whether any component is hosted externally, depends on the plant's architecture and requirements.
| Component | Intended responsibility | Design question |
|---|---|---|
| Support endpoint | Originate the approved session | What endpoint conditions can be verified, and what remains unknown? |
| Identity and authorisation | Establish individual identity and permitted task | Does approval constrain time, target and role? |
| Session gateway | Mediate access and apply supported session controls | Can the path be bypassed or used to reach additional destinations? |
| OT boundary controls | Restrict approved communications between zones | Are actual network rules consistent with the work scope? |
| Target environment | Enforce available local privileges | Does target access create persistent or wider authority? |
| Evidence service | Preserve relevant session and change records | Can records be correlated without overstating their coverage? |
The design should avoid implying that authentication alone secures the maintenance activity. Each component contributes a different control. A gateway cannot compensate for every target limitation, and a target account cannot establish whether the original connection followed the approved route.
Framework component 4
Specify identity and authority together
Proposed · requires local validation
Use individually attributable identities where feasible and document how vendor personnel are approved and removed. Authentication should be appropriate to the exposure, with strong multifactor methods where supported. The organisation must also establish how vendor personnel changes reach the access process.
Bind authorisation to the operational request. It should identify the target, intended task, work window and local approval. A vendor's commercial support entitlement is not sufficient to authorise every change to every machine.
Consider separate access profiles for diagnosis and change. A read-only route may be technically possible for some systems and unavailable for others. Where the tool cannot enforce a desired restriction, do not claim that it does; document the resulting authority and decide whether additional supervision or a different method is needed.
Review target credentials separately from gateway identities. A named remote user entering a shared engineering account may preserve individual attribution only to the extent the session and operating records can establish it. Check whether credentials can be reused through another route and whether the account outlives the approved work.
Framework component 5
Control tools and file movement
Proposed · requires local validation
Remote support often involves software packages, diagnostic outputs and configuration files. The proposed process should define which transfers are permitted, who authorises them and where files are checked before reaching the production target.
Use approved staging and validation suitable for the file type and equipment. Verify software provenance and the expected version, and follow engineering requirements for backup and rollback. A generic malware check is useful in some contexts but does not establish functional compatibility or safe process behaviour.
Diagnostic exports may contain plant configuration, credentials or commercially sensitive information. Define where the vendor may send them, which information is necessary and how retention is handled. An approved support session should not automatically authorise unrestricted data export.
Where legacy tools require features that increase reach or privilege, capture the limitation in the access record. Isolate the function as far as practical, time-bound its use and plan how to improve it. The existence of a tool requirement is a design input to assess, rather than a permanent exemption from oversight.
Framework component 6
Integrate the session with engineering change control
Proposed · requires local validation
Before connecting, operations should confirm the equipment state and any maintenance conditions. The work request should distinguish diagnosis from an actual change and identify who can approve an expansion of scope during the session.
During work, the local coordinator should be able to identify the participants, understand the current activity and reach the relevant operational owner. The level of supervision should reflect the task and equipment. Continuous observation may be justified for one activity and impractical or unnecessary for another; record the selected arrangement.
After a change, the engineering owner should perform the agreed verification before accepting completion. Preserve the relevant configuration or version record and document unexpected effects. Cybersecurity approval of the connection does not replace engineering acceptance of the result.
If the vendor discovers a need outside the approved scope, pause and obtain the appropriate authorisation. The process should be practical enough to use during maintenance, with a clear escalation route. A cumbersome ordinary process can encourage unrecorded exceptions unless urgent work is explicitly designed for.
Framework component 7
End access safely and completely
Proposed · requires local validation
Define the normal ending sequence, timeout behaviour and emergency isolation process. Establish what each action affects: a user session, a remote tool, a network route or a broader service. Plant personnel should understand the expected operational consequence.
Session expiry does not necessarily remove accounts, scheduled tasks or installed software. The closure record should identify access created or changed during the work and establish what remains authorised. Check target-side arrangements as well as the gateway.
Test the disconnect function in an appropriate controlled setting. A successful command to terminate access is only part of the evidence; verify the resulting connection state and whether the production process remains in its expected condition. Operational effects should be assessed by qualified personnel.
Define who may initiate an emergency isolation and who coordinates the plant response. Avoid a blanket instruction that the security team should automatically disconnect all OT access whenever an alert appears. The response must reflect both the threat and the operational conditions.
Framework component 8
Protect the access platform as a critical dependency
Proposed · requires local validation
Centralising access can improve consistency, but it also concentrates control. A compromised policy administrator or unavailable gateway can affect several vendor relationships. Include this platform in security, recovery and administrative-access reviews.
Separate management access from ordinary support sessions. Review who can change policies, approve their own privileges or suppress evidence. Protect recovery configurations and verify that authorised staff can restore the platform without relying on the same unavailable dependency.
Plan for loss of the access service. The approved response might use local support, defer work or activate a tightly controlled alternative. A permanent unrestricted bypass weakens the design. If an emergency route is necessary, document its prerequisites, owner, permitted scope and closure evidence.
The availability objective should reflect how the plant uses remote support. A monitoring-only service and an urgent engineering intervention may require different arrangements. The architecture should make that decision visible instead of relying on a default product configuration.
Framework component 9
Preserve evidence with realistic coverage
Proposed · requires local validation
Keep records that connect a session to the work request, approved individual, target and outcome. Depending on the technology, useful evidence may include authentication events, gateway records, network metadata, configuration changes and engineering acceptance.
Distinguish connection evidence from command or action evidence. A recording may show a screen without establishing every operation on the target. Encrypted or proprietary protocols can limit inspection. State these limits rather than claiming complete visibility.
Synchronised timestamps and an identifiable work reference improve correlation. Assign responsibility for reviewing alerts and exceptions; collecting logs without a review route provides limited operational assurance. Protect sensitive recordings and define access and retention according to the plant's actual requirements.
Framework component 10
Validate through bounded tests
Proposed · requires local validation
The following proposed test matrix is intended for adaptation in a lab or approved maintenance setting. Safe test methods and expected operational effects must be agreed before execution.
| Test | Intended observation | Acceptance owner |
|---|---|---|
| Approved task | Authorised participant can perform the agreed activity | Engineering owner |
| Out-of-scope reach | Safe verification shows destination constraints work as designed | OT network owner |
| Work-window expiry | Access ends or transitions according to the approved design | Operations and security |
| Personnel revocation | Removed vendor identity cannot resume the approved route | Identity owner |
| File transfer | Approved staging and destination restrictions behave as intended | Engineering and security |
| Emergency isolation | The agreed mechanism closes access with expected operational effects | Plant owner |
| Platform outage | Staff can follow the approved response without improvising a bypass | Operations lead |
| Closure review | Records connect the task, access and accepted result | Maintenance owner |
Testing should produce specific findings. A failed destination restriction requires technical correction or a revised approved boundary. An unclear isolation authority requires governance work. A logging gap may require a narrower assurance claim while a proportionate improvement is planned.
Do not generalise from one successful route to the whole estate. Identify the vendors, protocols, equipment and conditions covered. Retest after changes that could alter the result, such as access-platform upgrades, new remote tools or significant plant network modifications.
Framework component 11
Migrate through a controlled pilot
Proposed · requires local validation
During the first month, choose one production area and document its support uses and current routes. Establish ownership, operational constraints and supplier participation. Classify unknowns and select verification methods that are appropriate for the equipment.
During the second month, design the target path and session process. Include files, target privileges, local approval, normal closure and emergency handling. Review the design with operations, engineering, security and relevant suppliers before implementing changes.
During the third month, validate representative sessions in the approved setting. Record findings, refine the process and determine which old routes can be retired safely. Where retirement depends on a supplier change, keep the exception visible with interim controls and a review date.
Expand in stages based on operational consequence and implementation readiness. A group-wide rollout should preserve site differences and maintenance windows. Avoid counting a site as complete simply because a gateway has been installed.
Framework component 12
Governance and management evidence
Proposed · requires local validation
The plant owner is accountable for the operational boundary and acceptable consequences. Engineering defines and accepts equipment changes. OT architecture and security validate the access design and evidence. Supplier management coordinates commercial obligations and personnel changes. These roles need an agreed escalation route for unresolved tradeoffs.
Useful indicators include approved routes with confirmed owners, active exceptions past review date, sessions linked to a work request and target-side access left open after completed work. Define the denominator and evidence period for each measure.
Management should also see access-platform dependencies and validation gaps. A high percentage of sessions using the central gateway does not establish that alternate routes are closed. Combine adoption measures with evidence about actual reach and closure.
Framework component 13
A practical exception record
Proposed · requires local validation
Legacy equipment and support constraints can prevent immediate adoption of the target design. The proposed exception record should state the equipment, route, operational purpose, technical limitation and consequences of withdrawing access. Name both the operational acceptance owner and the person responsible for the improvement plan.
Describe compensating measures precisely. “Monitored access” should identify what is observed, by whom, during which period and with what response authority. “Temporary access” should identify the mechanism that ends it and the evidence of closure. If either condition cannot be demonstrated, retain that as an unresolved limitation.
Include the conditions under which the exception must be reconsidered. A new support tool, equipment replacement, change in vendor or expanded network reach can invalidate the original acceptance. Review dates should not become automatic renewals without checking whether the assumptions remain true.
An exception is a management decision within a defined boundary. It should not silently become the default architecture for additional equipment. Where several sites share the same limitation, consider a coordinated engineering solution while preserving site-specific operating approval.
Framework component 14
Procurement questions for new equipment
Proposed · requires local validation
New equipment is an opportunity to reduce future access constraints. Before selection, ask the supplier to demonstrate its support route, identity options, required privileges, file-transfer process and available records. Establish which functions remain usable without an external connection and what happens when the supplier's support service is unavailable.
Request a description of how remote access is enabled and disabled, how supplier personnel changes are handled and how customer authorisation is enforced. Identify any account or connection that the supplier expects to retain permanently. Confirm how updates and support tools interact with the plant's engineering change process.
Treat demonstrations as evidence with a scope. A supplier showing a feature in its own environment does not establish integration with the plant's network and identity design. Record the acceptance checks needed during commissioning and before production use.
Build route registration, documentation handover and closure testing into commissioning. Assign responsibility for removing temporary installation access after acceptance. This gives the plant a clear starting record and avoids leaving commissioning arrangements outside the normal operating process.
5Implementation and validation
Recommendations are ordered by priority. Effort is a broad estimate for a mid-sized organisation; your own will depend on what is already in place.
| # | Recommendation | Owner | Priority | Effort | Framework reference |
|---|---|---|---|---|---|
| 1 | Register all remote support routes for one production area, including alternate connectivity. | OT engineering owner | High | Medium | CSA OT Masterplan; NCSC connectivity Principle 3 |
| 2 | Bind each support approval to a person, task, target and work window. | Maintenance lead with security | High | Medium | NIST SP 800-82r3 remote-access guidance |
| 3 | Validate the normal and emergency closure process with engineering oversight. | Plant owner | High | Medium | NIST SP 800-82r3 AC-17(9) discussion |
| 4 | Track legacy exceptions and retire redundant routes through controlled change. | OT architecture and supplier manager | Medium | Medium | NCSC connectivity Principle 3 |
During the first month, choose one production area and document its support uses and current routes. Establish ownership, operational constraints and supplier participation. Classify unknowns and select verification methods that are appropriate for the equipment.
During the second month, design the target path and session process. Include files, target privileges, local approval, normal closure and emergency handling. Review the design with operations, engineering, security and relevant suppliers before implementing changes.
During the third month, validate representative sessions in the approved setting. Record findings, refine the process and determine which old routes can be retired safely. Where retirement depends on a supplier change, keep the exception visible with interim controls and a review date.
Expand in stages based on operational consequence and implementation readiness. A group-wide rollout should preserve site differences and maintenance windows. Avoid counting a site as complete simply because a gateway has been installed.
| Action | Completion evidence |
|---|---|
| Register all remote support routes for one production area, including alternate connectivity. | Route register with evidence dates and owners. |
| Bind each support approval to a person, task, target and work window. | Approved request and constrained route demonstrated. |
| Validate the normal and emergency closure process with engineering oversight. | Connection state and expected operational effects verified. |
| Track legacy exceptions and retire redundant routes through controlled change. | Exception review and documented retirement evidence. |
Download the assessment worksheet (CSV) · Download the framework diagram (SVG) · Download the source register (JSON)
Companion report: Remote vendor access to production systems: where control needs verification.
6Limitations
- This is a qualitative synthesis of the four primary sources cited in section 1, with original proposed architecture and operating practices. No equipment, configurations, incident data or vendor products were tested. No reduction in incidents, cost or downtime was measured. This paper does not establish compliance with any sector-specific obligation or suitability for a particular safety environment.
- The architecture's effectiveness depends on implementation, equipment capabilities and site conditions. Qualified OT engineering and technical personnel must validate the design and source applicability locally before implementation.
- The framework has not been independently peer reviewed or empirically validated. Regulatory references reflect sources checked on 11 November 2026 and may change; readers must determine current applicability.
7How to use this whitepaper
Design principles are proposed practices, not measured findings. Confidence concerns the support for an analytical judgement, not a numerical probability of an incident. No likelihood estimates are made. Hypothetical examples and conceptual diagrams do not establish prevalence or effectiveness. References describe source guidance; worksheets and implementation steps are proposed tools.
- High confidence
- Based on good-quality information from several independent sources, or on a complete dataset. A high-confidence judgement can still be wrong.
- Moderate confidence
- Based on credible information, but with gaps, a limited sample or more than one plausible interpretation.
- Low confidence
- Based on scarce, fragmented or single-source information. Treat it as something to watch, not as the sole basis for a major decision.
8References
- Cyber Security Agency of Singapore. (2024). Singapore’s Operational Technology Cybersecurity Masterplan 2024. https://www.csa.gov.sg/resources/publications/singapore-s-operational-technology-cybersecurity-masterplan-2024/
- Stouffer et al. (2023). Guide to Operational Technology (OT) Security. NIST SP 800-82 Rev. 3. https://nvlpubs.nist.gov/nistpubs/SpecialPublications/NIST.SP.800-82r3.pdf
- UK National Cyber Security Centre. (2026). Secure connectivity principles for OT: Principle 3, Centralise and standardise network connections. https://www.ncsc.gov.uk/collection/operational-technology/secure-connectivity/principle-3
- CISA and partners. (2025). Primary Mitigations to Reduce Cyber Threats to Operational Technology. 6 May 2025. https://www.cisa.gov/sites/default/files/2025-05/fact-sheet-primary-mitigations-to-reduce-cyber-threats-to-operational-technology-508c.pdf
9About this whitepaper
- Author
- Fahad Imran, Effycace Solutions
- Funding and interests
- Published by Effycace Solutions with Fahad Imran as author. Prepared using AI-assisted research and drafting from the cited public sources. No client information was used. No independent peer review or operational evaluation was conducted.
- Distribution
- TLP:CLEAR This report may be shared freely, with attribution.
- Corrections
- If you find an error, write to contact@effycace.com. Corrections are recorded in the version history below.
How to cite
Fahad Imran (2026). Designing secure IT–OT access without disrupting production (Report EFF-WP-2026-003, version 1.0). Effycace Solutions Pte Ltd. https://www.effycace.com/research/reports/secure-it-ot-vendor-access-whitepaper/
Version history
| Version | Date | Change |
|---|---|---|
| 0.9 | 11 November 2026 | Integrated editorial draft with source register, conceptual diagram and assessment worksheet. Not published. |
| 1.0 | 12 November 2026 | First publication edition, with author attribution, explicit review limitations and supporting assessment materials. |
This report is general information, not advice for your specific circumstances. See our Terms of Use.